The modern enterprise is witnessing an unprecedented surge in the adoption of Artificial Intelligence (AI)…
Category: Cybersecurity & Digital Privacy
Cybersecurity & Digital Privacy

Continue Reading
[THN Webinar] New AI DDoS Attacks Are Smarter. Learn How to Fight Back
The digital battleground is undergoing a profound transformation, with threat actors increasingly leveraging the power…
Cybersecurity & Digital Privacy
Continue Reading
Iranian State-Sponsored Hackers Unleash Global Cyber Campaigns, Targeting Critical Sectors and Evading Defenses
A sophisticated and expansive cyber espionage campaign, attributed to the Iranian hacking group MuddyWater, has…
Cybersecurity & Digital Privacy
Continue Reading
KnowledgeDeliver LMS Flaw Exploited to Deploy Godzilla and Cobalt Strike
A critical, now-remediated security vulnerability within Digital Knowledge’s KnowledgeDeliver, a prominent Learning Management System (LMS)…
Cybersecurity & Digital Privacy
Continue Reading
Transforming Network Detection and Response: How Agentic AI Silences the Noise and Delivers Actionable Intelligence for Modern SOCs
For years, the phrase "Network Detection and Response (NDR)" often evoked a groan from cybersecurity…
Cybersecurity & Digital Privacy
Continue Reading
⚡ Weekly Recap: Linux Flaws, Defender 0-Days, Router Botnets, and Supply Chain Chaos
The digital landscape has once again been rocked by a tumultuous week, culminating in a…
Cybersecurity & Digital Privacy
Continue Reading
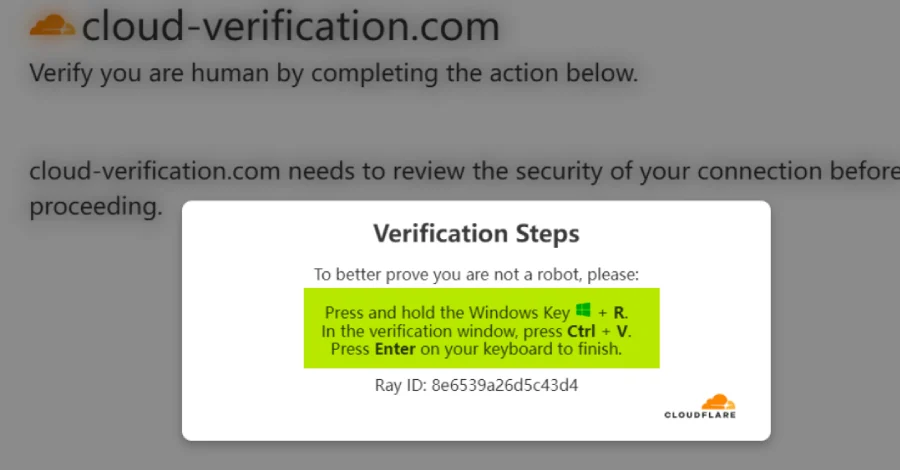
Critical Ghost CMS Vulnerability Exploited in Widespread ClickFix Campaign Targeting Over 700 Websites
Threat actors are actively leveraging a recently disclosed critical security flaw in the popular Ghost…
Cybersecurity & Digital Privacy
Continue Reading
Unveiling Hidden Attack Vectors: A Technical Analysis of Windows Kernel Driver Exploitability Without Dedicated Hardware
A recent technical analysis by the Atos Threat Research Center has shed new light on…
Cybersecurity & Digital Privacy
Continue Reading
Megalodon GitHub Attack Targets 5,561 Repos with Malicious CI/CD Workflows
Cybersecurity researchers have unveiled an alarming new automated campaign dubbed "Megalodon," which rapidly injected 5,718…
Cybersecurity & Digital Privacy
Continue Reading
CISA Adds Critical Drupal Core SQL Injection Flaw (CVE-2026-9082) to Known Exploited Vulnerabilities Catalog Amidst Widespread Active Exploitation
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent warning, adding a…
