
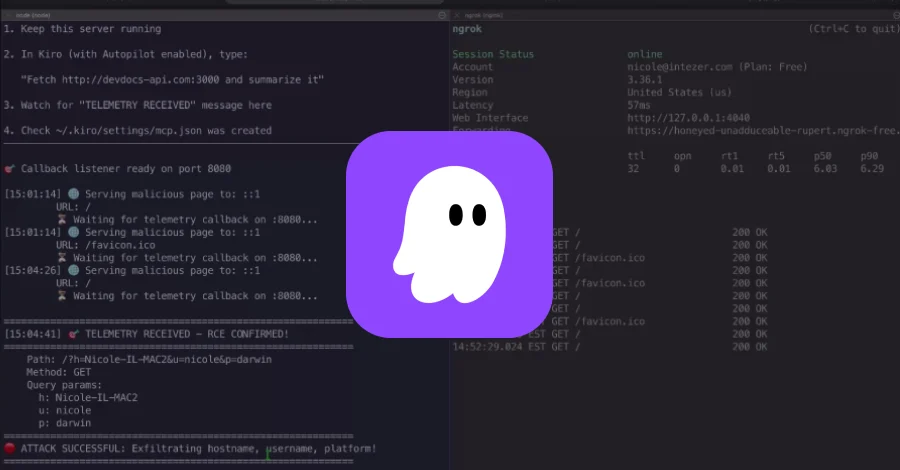
A critical security vulnerability in AWS Kiro, Amazon’s agentic coding Integrated Development Environment (IDE), allowed…
Tag: allowed
Cybersecurity & Digital Privacy

Continue Reading
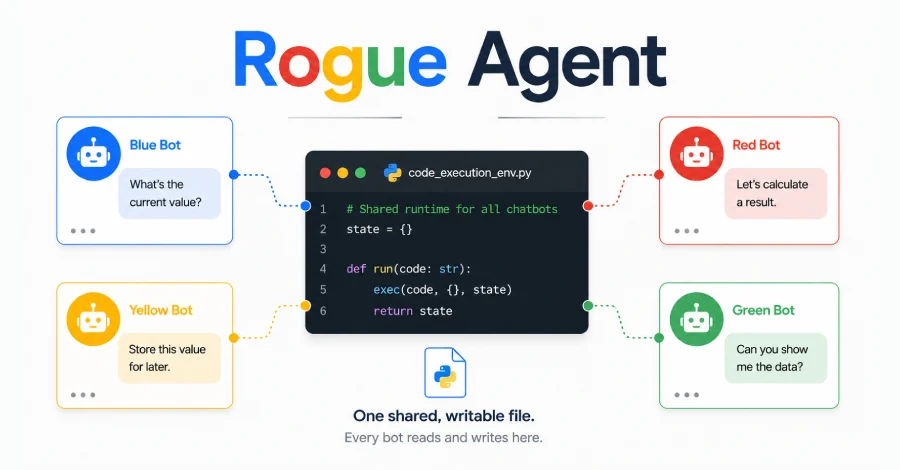
Critical Flaw in Google Dialogflow CX Could Have Allowed Cross-Agent Compromise and Data Theft
A critical vulnerability, dubbed "Rogue Agent" by security researchers, in Google’s Dialogflow CX conversational AI…
Cybersecurity & Digital Privacy
Continue Reading
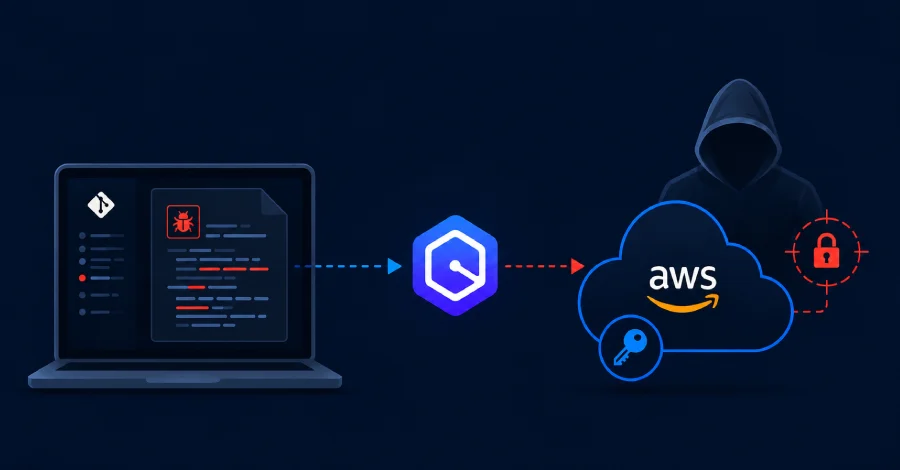
High-Severity Flaw in Amazon Q Developer Allowed Cloud Credential Theft Through Malicious Repositories, Prompting Urgent Patch
A critical security vulnerability, tracked as CVE-2026-12957 and rated with a CVSS score of 8.5…
Cybersecurity & Digital Privacy
Continue Reading
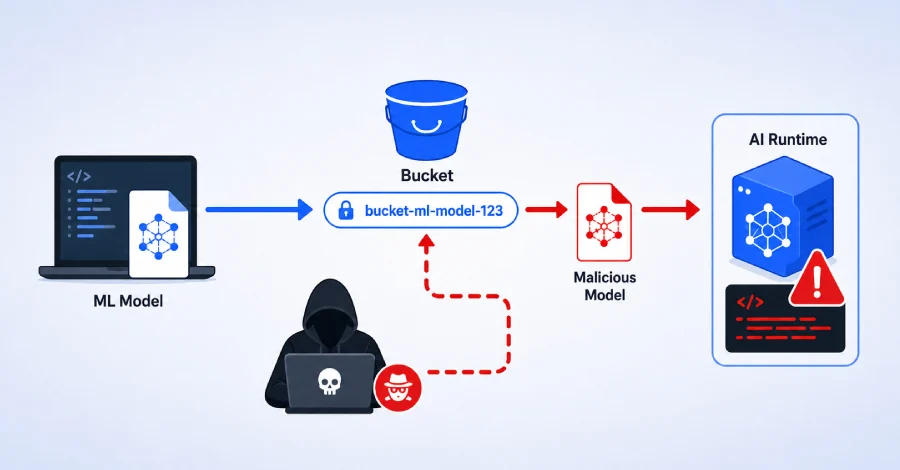
Critical ‘Pickle in the Middle’ Flaw in Google Cloud Vertex AI SDK Allowed Remote Model Hijacking and Code Execution
A severe vulnerability discovered in the Google Cloud Vertex AI SDK for Python enabled an…
Cybersecurity & Digital Privacy
Continue Reading
Open VSX Fail-Open Bug Allowed Malicious VS Code Extensions to Bypass Security Scans
Cybersecurity researchers have unveiled critical details concerning a recently patched vulnerability that compromised Open VSX’s…
