
A severe vulnerability has been identified within the core of WordPress, allowing an anonymous HTTP…
Tag: authentication
Cybersecurity & Digital Privacy

Continue Reading
Critical SimpleHelp Authentication Bypass Actively Exploited to Deliver Multi-Platform TaskWeaver Loader and Djinn Stealer Malware
An unknown threat actor has been observed actively exploiting a recently disclosed maximum-severity security flaw…
Cybersecurity & Digital Privacy
Continue Reading
Palo Alto Networks Warns of Active Exploitation in GlobalProtect Authentication Bypass Vulnerability (CVE-2026-0257)
Palo Alto Networks has issued an urgent warning regarding a recently disclosed medium-severity security flaw,…
Cybersecurity & Digital Privacy
Continue Reading
Cisco Issues Urgent Patches for Critical SD-WAN Authentication Bypass Actively Exploited in the Wild
Cisco has released crucial security updates to address a maximum-severity authentication bypass vulnerability, tracked as…
Cybersecurity & Digital Privacy
Continue Reading
Critical PraisonAI Authentication Bypass Exploited Within Hours of Disclosure, Highlighting Urgent API Security Risks
A severe security vulnerability identified as CVE-2026-44338 within PraisonAI, an emerging open-source multi-agent orchestration framework,…
Cybersecurity & Digital Privacy
Continue Reading
Progress Software Issues Urgent Updates for Critical Authentication Bypass and Privilege Escalation Flaws in MOVEit Automation
Progress Software, a leading provider of application development and digital experience technologies, has released critical…
Data Center & Server Infrastructure

Continue Reading
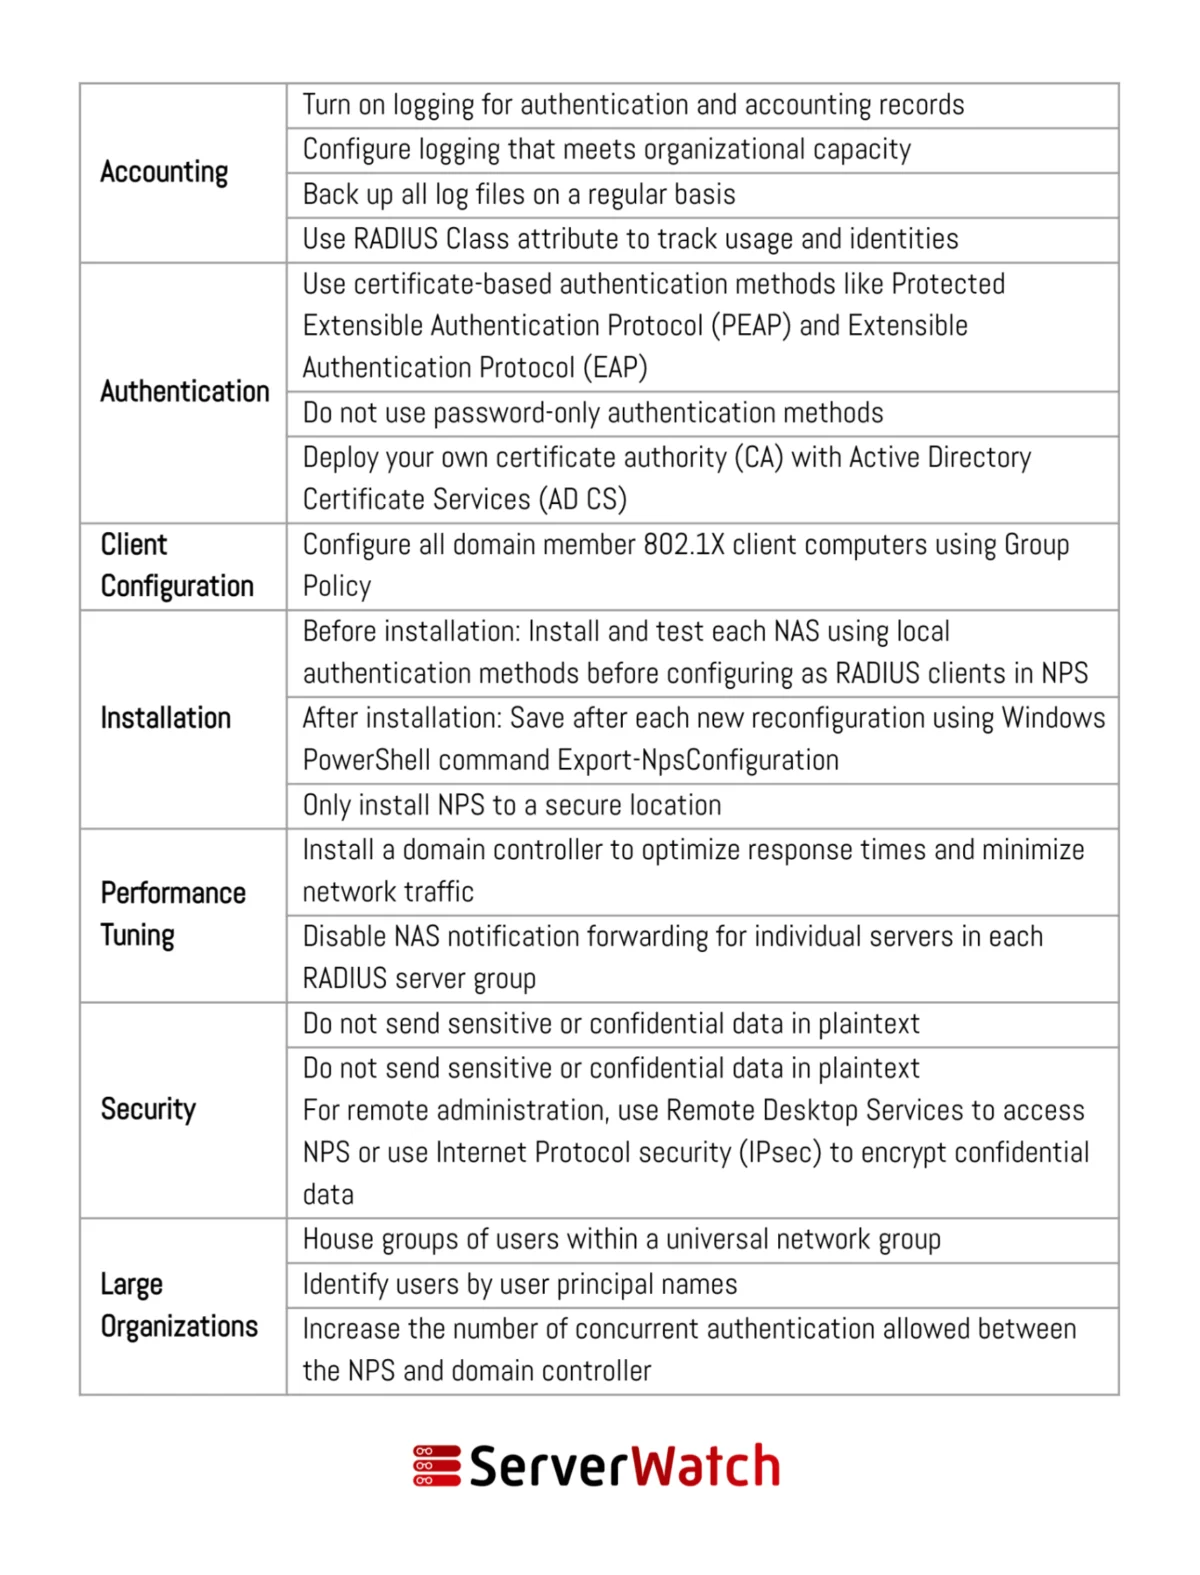
Network Policy Server (NPS) Fortifies Network Security Through Centralized Authentication, Authorization, and Accounting
In an era of escalating cyber threats and increasingly complex network infrastructures, organizations are continuously…
Cybersecurity & Digital Privacy
Continue Reading
Critical Authentication Bypass in Nginx-UI (CVE-2026-33032) Under Active Exploitation, Threatening Thousands of Web Servers Globally.
A severe security vulnerability, identified as CVE-2026-33032 and codenamed "MCPwn" by Pluto Security, has been…
Cybersecurity & Digital Privacy
Continue Reading
Cisco Addresses Critical Authentication Bypass and Remote Code Execution Vulnerabilities Across Key Enterprise Products
The technology giant Cisco Systems has issued urgent security updates to mitigate two critical vulnerabilities,…
