In a landmark and alarming development within the cybersecurity landscape, security firm Sysdig has reported…
Tag: Cybercrime
Cybersecurity & Digital Privacy

Continue Reading
Critical Unpatched Vulnerability in Argo CD’s Repo-Server Exposes Kubernetes Clusters to Unauthenticated Remote Code Execution and Full Takeover.
A significant security flaw has been identified in Argo CD, a widely adopted open-source continuous…
Cybersecurity & Digital Privacy
Continue Reading
Brazilian Banking Trojan Ousaban Intensifies Attacks on Windows Users Across Spain and Portugal with Advanced Evasion Tactics
A sophisticated campaign involving the Brazilian banking trojan, Ousaban, has been identified targeting Windows users…
Cybersecurity & Digital Privacy
Continue Reading
Microsoft Azure CLI Under Attack: Deprecated OAuth Flow Exploited in Massive Password Spray Campaign
Cybersecurity researchers have issued a stark warning regarding a "massive, ongoing, automated password spray attack"…
Cybersecurity & Digital Privacy
Continue Reading
Langflow RCE Exploited to Deploy Monero Miner on Exposed AI App Endpoints
Cybersecurity researchers have uncovered an ongoing campaign where threat actors are actively exploiting a critical…
Cybersecurity & Digital Privacy
Continue Reading
Critical SimpleHelp Authentication Bypass Actively Exploited to Deliver Multi-Platform TaskWeaver Loader and Djinn Stealer Malware
An unknown threat actor has been observed actively exploiting a recently disclosed maximum-severity security flaw…
Cybersecurity & Digital Privacy
Continue Reading
Oracle E-Business Suite Flaw CVE-2026-46817 Actively Exploited in the Wild
On June 30, 2026, cybersecurity firm Defused Cyber issued an alert confirming that the high-severity…
Cybersecurity & Digital Privacy
Continue Reading
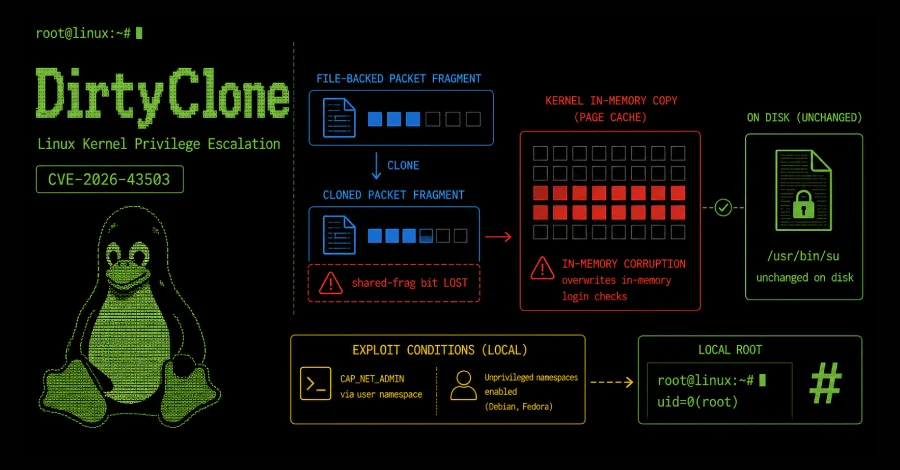
New ‘DirtyClone’ Linux Kernel Vulnerability (CVE-2026-43503) Allows Local Privilege Escalation, Exploits ‘DirtyFrag’ Family Flaws for Root Access
A critical new local privilege escalation vulnerability, dubbed "DirtyClone" and tracked as CVE-2026-43503, has been…
Cybersecurity & Digital Privacy
Continue Reading
Critical RCE Vulnerability in PTC Windchill and FlexPLM Actively Exploited, CISA Adds to KEV Catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday, June 25, 2026, issued a…
Cybersecurity & Digital Privacy
Continue Reading
High-Severity Flaw in Amazon Q Developer Allowed Cloud Credential Theft Through Malicious Repositories, Prompting Urgent Patch
A critical security vulnerability, tracked as CVE-2026-12957 and rated with a CVSS score of 8.5…
