
In a significant victory against sophisticated cybercrime, a formidable alliance comprising CrowdStrike, Google, and the…
Tag: supply
Cybersecurity & Digital Privacy

Continue Reading
⚡ Weekly Recap: Linux Flaws, Defender 0-Days, Router Botnets, and Supply Chain Chaos
The digital landscape has once again been rocked by a tumultuous week, culminating in a…
Cybersecurity & Digital Privacy
Continue Reading
A Coordinated Supply Chain Attack Targets Packagist, Deploying Malicious Linux Binaries Through Cross-Ecosystem Package Manipulation
A sophisticated and coordinated supply chain attack campaign has recently been uncovered, impacting at least…
Cybersecurity & Digital Privacy
Continue Reading
GitHub Introduces Staged Publishing and Enhanced Install Controls to Fortify npm Software Supply Chain Security
GitHub, the world’s leading platform for software development and version control, has announced a significant…
Cybersecurity & Digital Privacy
Continue Reading
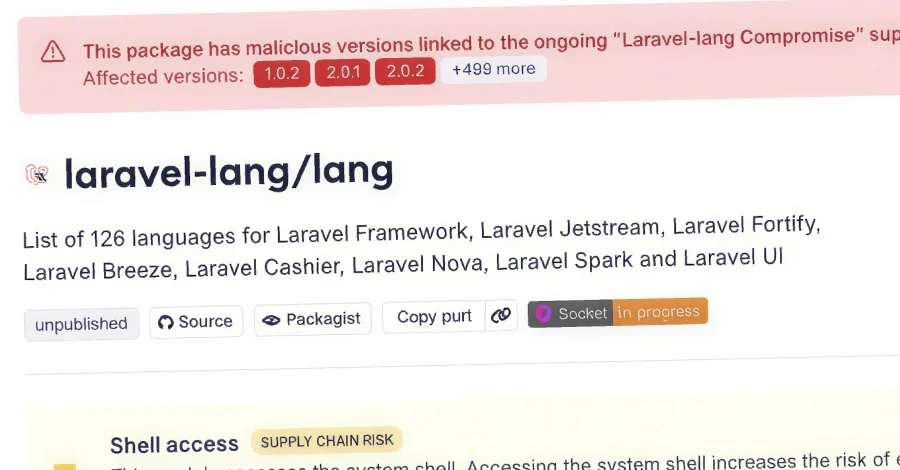
Laravel-Lang Targeted in Sophisticated Supply Chain Attack Delivering Comprehensive Credential-Stealing Framework
Cybersecurity researchers have recently identified and flagged a sophisticated software supply chain attack campaign that…
Digital Transformation & Strategy

Continue Reading
Blue Yonder Redefines Supply Chain Architecture through Owned Intelligence and Agent-Centric Operations at ICON 2026
The global supply chain landscape is currently undergoing a fundamental architectural shift, moving away from…
Enterprise Software & DevOps

Continue Reading
2025: The Year AI Redefined Software Supply Chain Security, Ushering in Unprecedented Risks
The year 2025 marked a seismic shift in the digital landscape, not only by witnessing…
Cybersecurity & Digital Privacy
Continue Reading
Exploiting Trust: The Pervasive Threat of Supply Chain and Identity Attacks in Modern Cybersecurity
This week, the cybersecurity landscape once again demonstrated a subtle yet profound shift in attacker…
Cybersecurity & Digital Privacy
Continue Reading
GitHub Confirms Major Internal Breach Stemming from Poisoned VS Code Extension and Widespread Supply Chain Attack
GitHub officially confirmed on Wednesday, May 21, 2026, that a significant breach of its internal…
Blockchain & Web3

Continue Reading
Shai-Hulud Malware Campaign Highlights Perilous Reliance on Automated Software Supply Chains
A sophisticated malware campaign, dubbed "Shai-Hulud," is silently infiltrating the automated pipelines developers rely on…
