
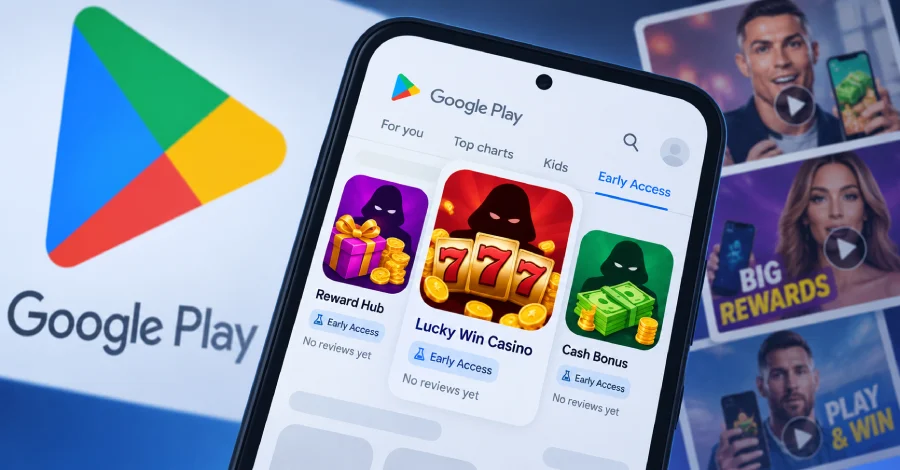

The Google Play Store’s Early Access program, originally designed to foster innovation and facilitate developer-user collaboration, has become a hotbed for cybercriminal activity. Threat actors are increasingly exploiting the unique mechanics of this sandbox environment to distribute deceptive applications that promise fraudulent financial rewards, counterfeit casino experiences, and illicit premium content. By bypassing the traditional scrutiny applied to fully released applications, these bad actors have successfully bypassed safety nets, exposing millions of users to aggressive advertising, data harvesting, and sophisticated financial scams.
The Architecture of the Vulnerability
At its core, the Early Access program allows developers to publish applications that are still in the testing or development phase. This enables them to gather essential feedback and telemetry before a wider public launch. However, a fundamental design choice—the omission of public reviews and star ratings—has created a critical security loophole. Because these applications are excluded from the standard user-feedback loop, the "trust signals" that typically warn users of potential threats are absent.
Cybersecurity researchers at Bitdefender have identified this as a strategic exploit. In a standard marketplace environment, a wave of one-star reviews or warnings regarding a scam app would alert both the community and Google’s automated moderation systems. In the Early Access ecosystem, however, these apps operate in a vacuum. Users are deprived of the collective wisdom of the community, leaving them susceptible to polished, high-production-value scams that appear legitimate upon first glance.
A Growing Trend of Deceptive Lures
The variety of fraudulent applications circulating through this channel is extensive. Investigators have cataloged a wide spectrum of lures, including:

- Financial Fraud: Apps promising immediate payouts via PayPal, cryptocurrency wallets, or gift cards.
- Casino and Gambling Mimicry: Illegal gambling platforms that mask themselves as benign puzzle or casual games to bypass regional age restrictions and licensing requirements.
- Utility Spoofing: Malicious versions of essential tools, such as QR code scanners, PDF converters, and device optimization software, which serve primarily as vehicles for relentless ad injection.
- Intellectual Property Infringement: Titles that trade on the popularity of established brands, such as the now-removed "Vice Streets: Open World," which leveraged the aesthetic of high-profile gaming franchises to amass over one million downloads.
The operational model for these apps is consistent. Victims are typically funneled to the Google Play Store via sophisticated social media campaigns on platforms like TikTok and Facebook. These advertisements frequently employ AI-generated deepfakes of celebrities or trusted public figures, creating a false sense of legitimacy and urgency. Once installed, the applications often provide a "honeypot" experience, rewarding the user with virtual currency or small, initial gains. However, as the user nears the threshold for actual cash withdrawal, the application’s functionality stalls, and the promised rewards are indefinitely withheld, leaving the developer to monetize the user’s continued engagement through invasive interstitial and banner advertisements.
Chronology of Exploitation and Escalation
The abuse of the Early Access program did not happen in a vacuum; it is the result of an evolving threat landscape where malicious developers have learned to navigate the friction points of app store policies.
In early 2026, security firms began documenting an uptick in "ghost apps" that would appear in the store for short bursts, harvest user data or ad revenue, and vanish before they could be flagged for manual review. By mid-2026, the strategy shifted toward long-term monetization. The use of deepfakes in promotional material, which became a significant concern in early 2024, has now merged with the Early Access exploit, providing a "triple threat" of social engineering, platform abuse, and technical obfuscation.
The removal of high-profile offenders, such as the "Vice Streets" title, highlights the reactive nature of the current defense strategy. While Google’s automated systems are designed to detect malware signatures, they often struggle to identify the intent of an application that is technically compliant with code standards but fraudulent in its business model.
Broader Implications for Mobile Security
The implications of this trend extend beyond simple financial loss for the end user. The ability for threat actors to distribute apps that masquerade as legitimate tools creates a systemic risk to the integrity of the Android ecosystem.

When users are repeatedly exposed to scams—particularly those that mimic familiar utilities—the general level of digital literacy and trust in the marketplace erodes. This climate of suspicion can inadvertently harm legitimate developers who use the Early Access program for its intended purpose. If the barrier to entry for malicious actors remains low, the entire program may eventually require a fundamental overhaul, potentially limiting the opportunities for honest developers to test their work.
Furthermore, this activity is occurring concurrently with an increase in sophisticated banking trojans, such as Gigabud. The rise of "companion apps" like Vwork—a tool that utilizes work profiles to hide malicious banking activity—suggests that the mobile threat landscape is becoming increasingly segmented. While Early Access scams focus on high-volume, low-effort ad revenue, more advanced actors are using similar distribution channels to plant the seeds for more devastating, long-term financial compromises.
The Call for Enhanced Oversight
The cybersecurity community, led by researchers at Bitdefender and others, has called for a reassessment of the Early Access review policies. While the protection of developers from "review bombing" is a valid concern, the current lack of transparency represents a greater risk to the security of the user base.
Potential solutions proposed by security analysts include:
- Limited Feedback Channels: Implementing a controlled, private feedback system that allows users to report suspicious behavior to Google without exposing developers to public review-bombing.
- Increased Verification Requirements: Mandatory identity verification for developers participating in Early Access, potentially tied to professional credentials or verified business entities.
- Enhanced AI-Driven Content Analysis: Utilizing advanced machine learning models to detect patterns in promotional material (such as deepfakes) that deviate from the actual content of the application.
Official Stance and Future Outlook
As of September 2026, the situation remains fluid. Google has historically maintained that it continuously updates its policies to combat bad actors, utilizing a combination of machine learning and manual review. However, the sheer volume of applications submitted to the Play Store daily presents an immense logistical challenge.

Industry observers note that the responsibility cannot lie solely with the platform operator. Social media companies, which serve as the primary marketing funnel for these scams, also face increasing pressure to verify the authenticity of advertisements that link to app stores. The integration of AI-generated content into ad campaigns has made it significantly harder for consumers to discern between authentic endorsements and predatory marketing.
As the industry waits for a definitive response from major stakeholders, the advice for users remains consistent: exercise extreme caution when downloading apps from Early Access, particularly those that promise financial incentives or feature highly polished advertisements. In the absence of reviews or ratings, the lack of transparency should be treated as a warning sign. The digital landscape is currently in a state where the "early bird" does not necessarily get the worm, but rather, becomes the target for those who have mastered the art of digital deception.
The security of the Android ecosystem will likely depend on a multi-layered defense strategy that balances the need for developer innovation with the non-negotiable requirement for user protection. Until such measures are implemented, the Early Access program will continue to be a primary focus for those who seek to profit from the erosion of digital trust.
