
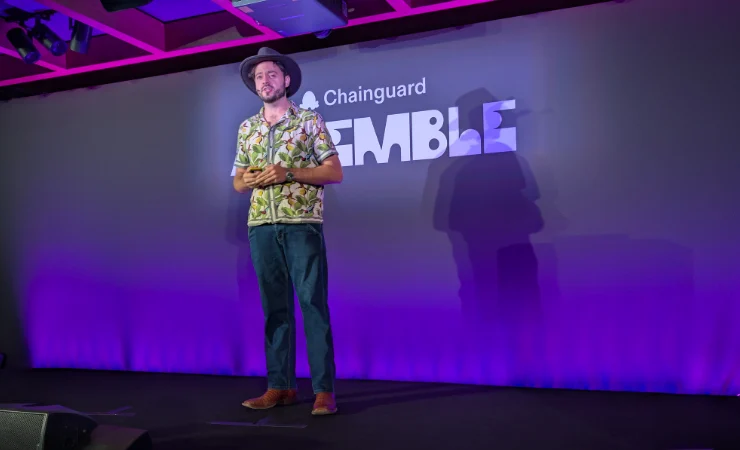

The landscape of software supply chain security is undergoing a fundamental structural evolution, moving past the traditional binary classification model of clean code versus outright malware. Speaking at the Chainguard Assemble conference in London this week, Chief Executive Officer Dan Lorenc introduced a third and increasingly disruptive category: grayware. This classification encompasses software that behaves identically to malicious code—such as credential theft, unauthorized data exfiltration, and telemetry monitoring—without technically violating terms of service because the operational behavior aligns with its stated purpose.
The announcement formed the centerpiece of a densely packed morning of product rollouts and strategic updates from the container security firm. Alongside the formalization of grayware policies, Chainguard showcased its autonomous security testing agent, dubbed Harness, detailed new compliance frameworks for post-quantum cryptography, and introduced regional container-serving options tailored to evolving international data regulations. The conference, held at Chainguard’s newly opened second physical office in London, drew a sold-out crowd of enterprise software leaders, featuring high-profile regional clients including Trustpilot, Nationwide Building Society, Depop, DoorDash, and Deliveroo.
The Emergence of Grayware in Public Package Registries
The traditional approach to software supply chain defense has relied heavily on signal-to-noise tuning, where security scanners attempt to isolate known malware while permitting legitimate codebases to flow through integration pipelines. However, Chainguard’s leadership argued that this reactive posture is no longer adequate in an era where automated tooling can harvest sensitive enterprise credentials within seconds of execution.
To illustrate the grayware phenomenon, Lorenc highlighted a prominent package discovered on npm, the public JavaScript package registry. The package installed a Chrome extension designed to automate outbound promotional messaging on LinkedIn by harvesting the user’s active session credentials. While the script functioned precisely as advertised—making it difficult for registry administrators to remove under standard terms of service—its underlying mechanics mirrored those of a credential-stealing Trojan.
Rather than allowing such software to execute unchecked, Chainguard’s updated platform logic approaches grayware through a default-deny paradigm, mirroring the "potentially unwanted programs" (PUPs) filters utilized by commercial antivirus software for over two decades. However, whereas a blocked PUP typically inconveniences an end user, blocking a component in an automated open-source software build pipeline can halt enterprise deployment entirely.
To mitigate operational disruption while enforcing security boundaries, the containment logic has been integrated into Chainguard’s Libraries product and its underlying policy engine. Enterprises can configure policy exceptions based on internal risk appetite, shifting the burden of trust away from passive registration and toward explicit organizational governance.
Autonomous Vulnerability Discovery: The Harness Framework
Among the most technically significant demonstrations at the London conference was a live walkthrough of Harness, an autonomous security testing engine designed to probe complex software architectures using generative AI and iterative tool calls. Prior to the keynote, Chainguard subjected vLLM—an open-source high-throughput serving engine for large language models—to a continuous 12-hour evaluation utilizing Harness.
The autonomous agent executed hundreds of tool calls and processed hundreds of millions of tokens, ultimately uncovering a critical vulnerability that allowed an unauthenticated attacker to manipulate output tokens directly in transit. During the live demonstration, a prompt asking for the capital of France yielded a randomized response of "Mango, mango." Because the manipulation occurred within the live token stream as it emerged from the model, the exploit remained entirely invisible to the end user.
The vulnerability was disclosed responsibly to the vLLM maintainers and successfully patched upstream prior to the keynote address. Crucially, Chainguard accompanied the disclosure by publishing a registry of complex codebases that Harness failed to compromise, including Curl, OpenSSH, and a newly developed sandboxing framework for Python.
Lorenc emphasized the strategic importance of transparency regarding codebases that successfully withstand automated exploits: "There are tons of people scanning these same projects, but we’re publishing the projects that have remediated all these vulnerabilities too, because we have a lot more confidence in using them, and we want to share that information with everyone."
This sentiment was echoed by Daniela Reed of Anthropic, who addressed the audience regarding the velocity of automated remediation. Reed noted that Mozilla successfully deployed 271 distinct patches in a single Firefox update after frontier AI models were applied systematically to the browser’s codebase. According to Reed, the primary operational bottleneck in modern software engineering has shifted definitively from discovering vulnerabilities to the administrative and engineering overhead required to apply fixes.
Sovereign Artifacts and Post-Quantum Cryptography Readiness
Addressing the intersection of geopolitics and enterprise compliance, Zane Lowitz, Chainguard’s product manager for compliance and cryptography, announced the launch of a sovereign artifacts beta program. The service provides dedicated EU-jurisdiction serving of container artifacts, addressing cross-border regulatory concerns that intensified following international export control directives.
Lowitz linked the initiative directly to recent geopolitical friction, noting that sudden regulatory shifts—such as restrictions placed on AI model access over the summer—demonstrated that enterprise data availability is frequently dictated by national policy rather than purely technological considerations.
Additionally, Chainguard introduced a FIPS Cryptographic Module Validation Program (CMVP) certificate covering forthcoming post-quantum cryptographic standards, including ML-KEM, ML-DSA, and SLH-DSA. These cryptographic modules are designed to align enterprises with upcoming compliance deadlines set by the Committee on National Security Systems, which mandates transitions to post-quantum stacks by January 1, 2027.
Operational Challenges in Upstream Remediation and Grayware Control
In discussions following the keynote, Lorenc elaborated on the systemic challenges surrounding grayware and coordinated vulnerability disclosure. He detailed a second instance of enterprise grayware discovered on npm: a comprehensive laptop monitoring utility published by a Chinese internet corporation. Operating essentially as a rootkit, the software was packaged with internal onboarding documentation in Mandarin, rendering its intent benign to its creators but hazardous within an uncontrolled enterprise development environment.
Furthermore, Lorenc noted that grayware categories frequently include hundreds of code wrappers and developer tool plugins designed to harvest authentication tokens. Because these utilities operate within the bounds of standard developer workflows, they bypass traditional malware filters, leaving security teams exposed to credential leakage.
However, default-blocking mechanisms are not infallible. Lorenc pointed to Anthropic’s distribution of Claude Code via npm as an operational hurdle during platform tuning. Because Claude Code is distributed as a closed-source binary that interacts deeply with system terminals, an overnight migration of its core codebase from the Zig programming language to Rust triggered Chainguard’s behavioral sensors. The rapid shift in execution patterns and the absence of accessible source code required localized policy adjustments to prevent build disruptions while preserving security oversight.
Coordinated vulnerability disclosure also remains an intricate friction point. Chainguard’s Athena pipeline—an industry coalition dedicated to coordinated vulnerability remediation—has processed more than 21,000 validated zero-day vulnerabilities. However, the efficacy of the pipeline depends entirely on the responsiveness of upstream maintainers. Lorenc acknowledged that while many open-source contributors react with gratitude, commercial vendors backing open-source projects have occasionally responded with formal complaints and legal notifications upon receiving automated vulnerability alerts.
The Broader Banking and Financial Coalition Response
The imperative for collaborative resilience was reinforced during the keynote by Craig Rice, Chief Executive Officer of the UK’s Cyber Defence Alliance (CDA). The CDA, a coalition uniting the world’s largest financial institutions for joint threat intelligence sharing, has contributed to nearly 500 arrests over a six-year period through coordinated target tracking.
Rice challenged traditional enterprise security paradigms, stating that individual institutional perimeter defense is no longer viable in an interconnected digital economy. "I can no longer defend that given space, let alone the value chains that flow through that space," Rice observed. "So the view that any one organisation is going to be able to defend itself in this ecosystem belongs in the dark ages."
Market Implications and Analytical Outlook
The integration of behavior-based grayware blocking marks a significant philosophical shift in software supply chain defense. For decades, security vendors have focused primarily on malice detection, relying on signatures and heuristic intent analysis after code has already entered the repository. By pivoting toward automated behavioral restriction by default, Chainguard is forcing organizations to define explicit operational boundaries.
However, this transition introduces complex administrative overhead. Security teams must now establish robust internal governance frameworks to evaluate blocked dependencies, tune policy exceptions, and prevent legitimate productivity tools from stalling critical release cycles.
As regulatory pressures mount—exemplified by impending post-quantum cryptographic mandates and increasing scrutiny over sovereign data jurisdictions—the capability to rapidly identify, test, and remediate software supply chain risks will serve as a primary differentiator for enterprise resilience. Organizations operating within highly regulated sectors, such as financial services and critical infrastructure, possess a structural advantage due to established compliance muscle memory. Yet, as the findings from the Chainguard Assemble conference demonstrate, the velocity of automated code generation and modern attack vectors requires continuous adaptation across the entire software development lifecycle.
