
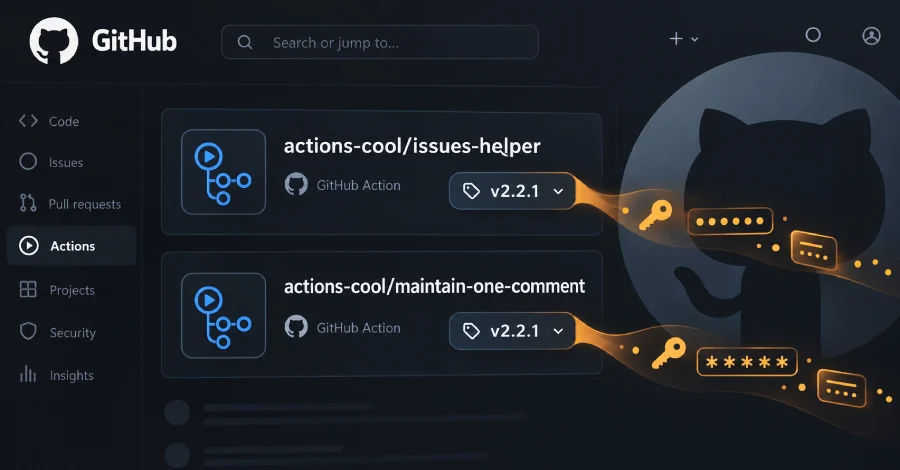
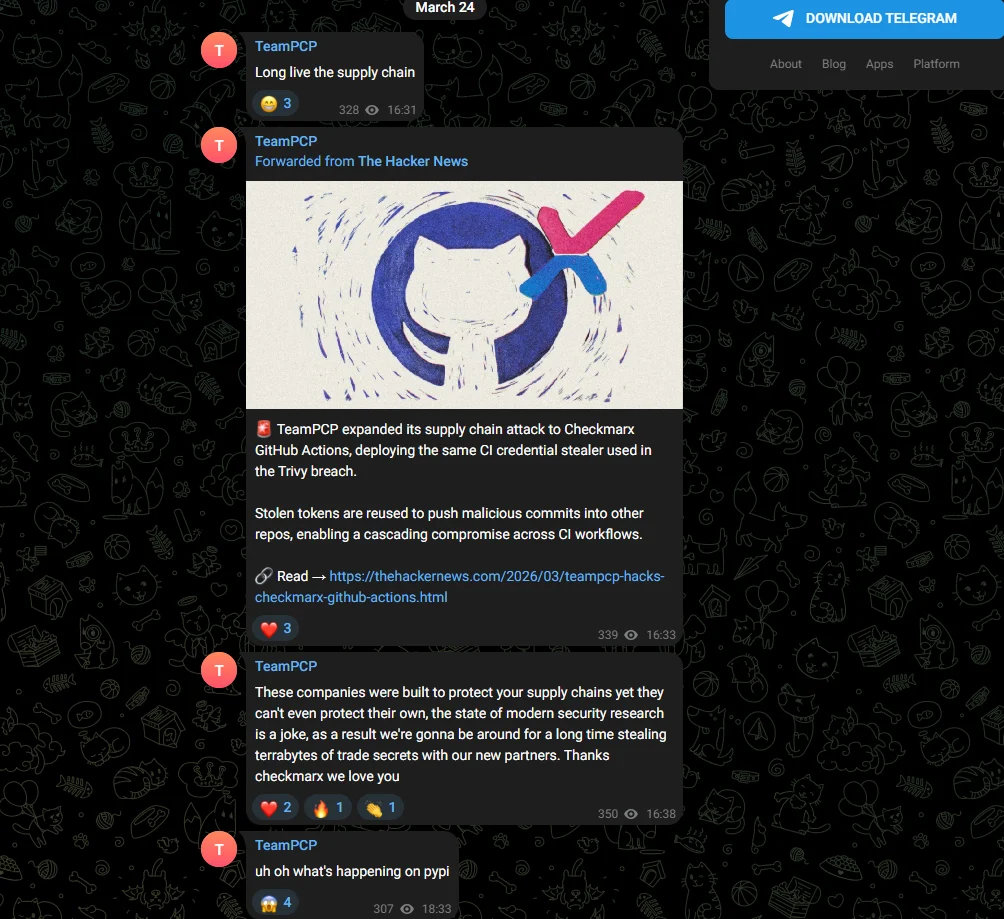
The Anatomy of the Re-Activation Incident The two GitHub Actions in question were originally compromised…
Tag: compromised
Cybersecurity & Digital Privacy

Continue Reading
Jscrambler npm Package Compromised with Infostealer, Exposing Developer Secrets and Raising Supply Chain Security Alarms
A critical security incident has rocked the JavaScript development ecosystem, with the popular jscrambler npm…
Cybersecurity & Digital Privacy
Continue Reading
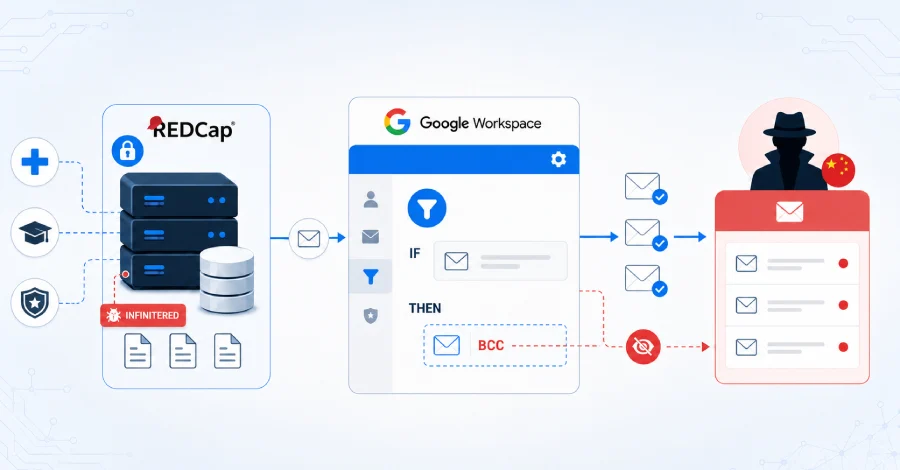
North American Research Networks Compromised by China-Linked Espionage Group in Year-Long Data Theft Campaign
A sophisticated, China-linked espionage group successfully infiltrated North American medical, academic, and military research networks…
Cybersecurity & Digital Privacy
Continue Reading
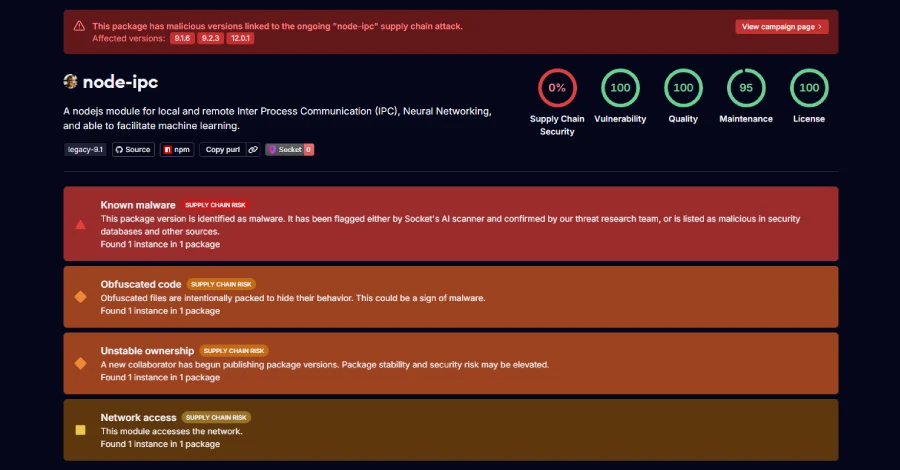
Cybersecurity Researchers Uncover Sophisticated Credential Stealer in Compromised Node-IPC npm Package
Cybersecurity researchers are sounding a definitive alarm regarding a highly sophisticated and deeply concerning malicious…
Cybersecurity & Digital Privacy
Continue Reading
OpenAI Employee Devices Compromised in Widespread Mini Shai-Hulud Supply Chain Attack Targeting Tech Giants
OpenAI, the pioneering artificial intelligence research and deployment company, has confirmed that two employee devices…
Cybersecurity & Digital Privacy
Continue Reading
Major Python Package "Lightning" Compromised in Sophisticated Supply Chain Attack Linked to TeamPCP and Mini Shai-Hulud Campaign
In a significant development echoing the escalating threats within the software ecosystem, the widely adopted…
Cybersecurity & Digital Privacy
Continue Reading
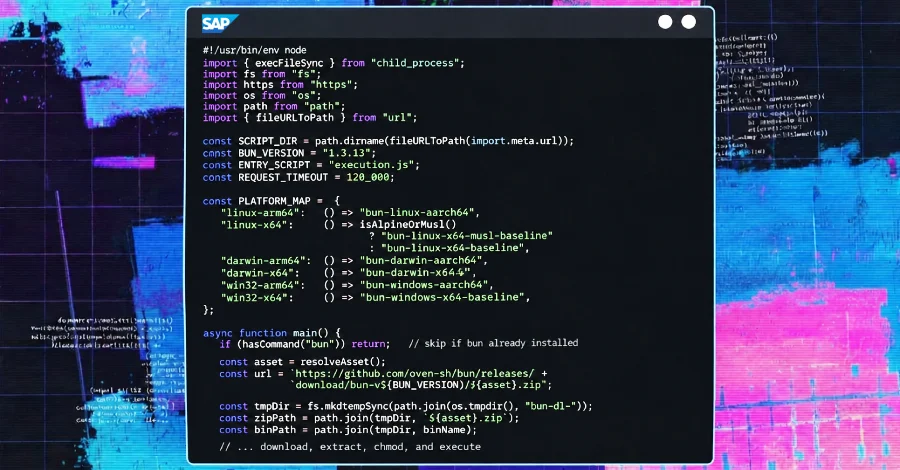
SAP-Related npm Packages Compromised in Sophisticated "mini Shai-Hulud" Supply Chain Attack
Cybersecurity researchers are sounding a critical alarm following the discovery of a sophisticated supply chain…
Cybersecurity & Digital Privacy
Continue Reading
Federal Agency’s Cisco Firepower Device Compromised by Persistent FIRESTARTER Malware in Widespread APT Campaign
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), in conjunction with the U.K.’s National Cyber…
Cybersecurity & Digital Privacy
Continue Reading
LiteLLM Python Package Compromised in Sophisticated TeamPCP Supply Chain Attack, Unveiling Credential Harvesters and Kubernetes Backdoors
The prominent Python package litellm, widely utilized for interfacing with various large language model (LLM)…
