
Cybersecurity researchers have unveiled a pair of critical security vulnerabilities affecting Ollama, a widely-adopted open-source…
Tag: critical
Cybersecurity & Digital Privacy

Continue Reading
Palo Alto Networks Discloses Critical PAN-OS Vulnerability Actively Exploited by Suspected State-Sponsored Actors.
Palo Alto Networks has issued an urgent advisory regarding a critical security flaw, CVE-2026-0300, within…
Semiconductors & Hardware

Continue Reading
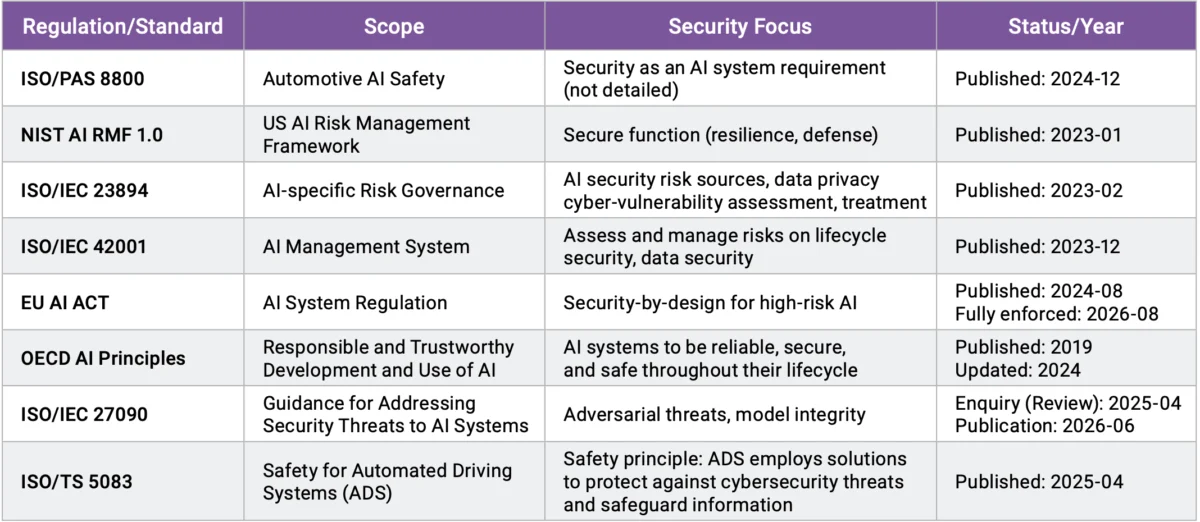
The Rapid Integration of Artificial Intelligence in Semiconductor Design and the Critical Gaps in Global Governance Frameworks
The global semiconductor ecosystem is currently undergoing a radical transformation as artificial intelligence is integrated…
Network Infrastructure & 5G

Continue Reading
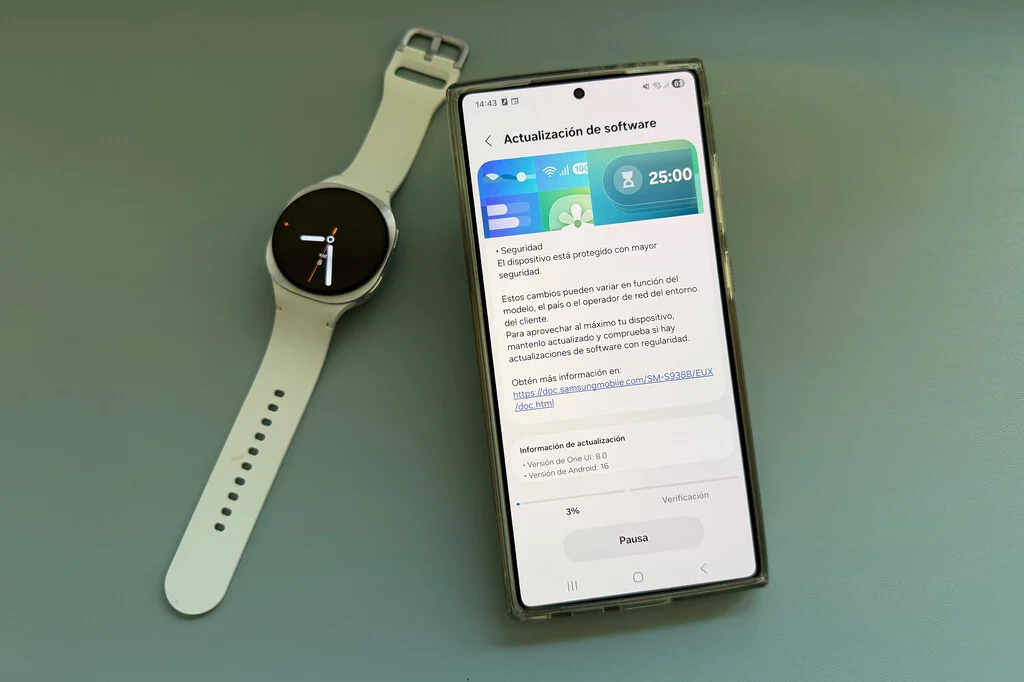
Samsung Begins Rollout of May 2024 Security Update for Galaxy Devices, Addressing Critical Vulnerabilities and Enhancing User Protection
The technology giant Samsung has officially commenced the deployment of its May 2024 security update…
Cybersecurity & Digital Privacy
Continue Reading
Critical Remote Code Execution Vulnerability Addressed in Apache HTTP Server 2.4.67 Update
The Apache Software Foundation (ASF) has released urgent security updates for its widely deployed HTTP…
Cybersecurity & Digital Privacy
Continue Reading
Cybersecurity Landscape Shifts to Persistent Occupation as Critical Flaws Fuel Exploitation Surge
The digital battleground has undeniably shifted, with threat actors demonstrating an alarming agility that consistently…
Cybersecurity & Digital Privacy
Continue Reading
Progress Software Issues Urgent Updates for Critical Authentication Bypass and Privilege Escalation Flaws in MOVEit Automation
Progress Software, a leading provider of application development and digital experience technologies, has released critical…
Cybersecurity & Digital Privacy
Continue Reading
Linux Kernel "Copy Fail" Vulnerability (CVE-2026-31431) Poses Critical Threat, Prompts Urgent CISA Alert and Patching Mandates.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday issued a pressing alert, adding…
Semiconductors & Hardware
Continue Reading
The Evolution of Hardware Security Verification and the Critical Role of Systematic Coverage Frameworks in Modern Semiconductor Design
Hardware security has transitioned from a niche concern reserved for military and financial applications into…
Cybersecurity & Digital Privacy
Continue Reading
Critical SQL Injection Vulnerability in LiteLLM Exploited Within 36 Hours of Public Disclosure, Threatening AI Gateway Security.
In a stark demonstration of the accelerating pace at which cyber adversaries move to leverage…
