
A newly identified, China-nexus cyber espionage group designated as TA419 has emerged as a significant…
Tag: credential
Cybersecurity & Digital Privacy

Continue Reading
High-Severity Flaws in OpenClaw AI Assistant Expose Users to Credential Theft, Privilege Escalation, and Remote Code Execution via External Messaging.
Details have emerged regarding three critical security vulnerabilities recently patched in the OpenClaw personal artificial…
Cybersecurity & Digital Privacy
Continue Reading
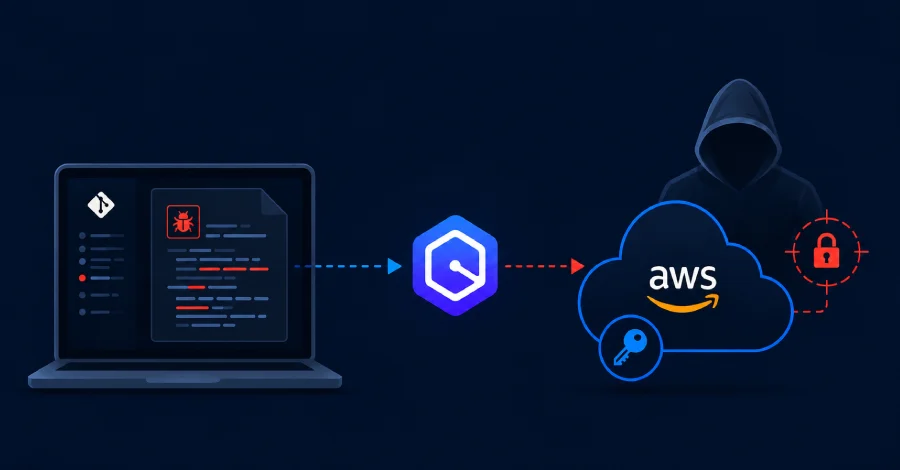
High-Severity Flaw in Amazon Q Developer Allowed Cloud Credential Theft Through Malicious Repositories, Prompting Urgent Patch
A critical security vulnerability, tracked as CVE-2026-12957 and rated with a CVSS score of 8.5…
Cybersecurity & Digital Privacy
Continue Reading
FortiBleed: Russian-Speaking Threat Actor Orchestrates Global Credential-Harvesting Campaign Targeting Over 430,000 FortiGate Firewalls and Beyond
A sophisticated, financially motivated Russian-speaking initial access broker (IAB) has been identified as the orchestrator…
Cybersecurity & Digital Privacy
Continue Reading
Extensive Supply Chain Attack Compromises Over 400 Arch User Repository Packages, Deploying Advanced Credential Stealer and eBPF Rootkit.
In a sophisticated supply chain attack that sent ripples through the open-source community, malicious actors…
Cybersecurity & Digital Privacy
Continue Reading
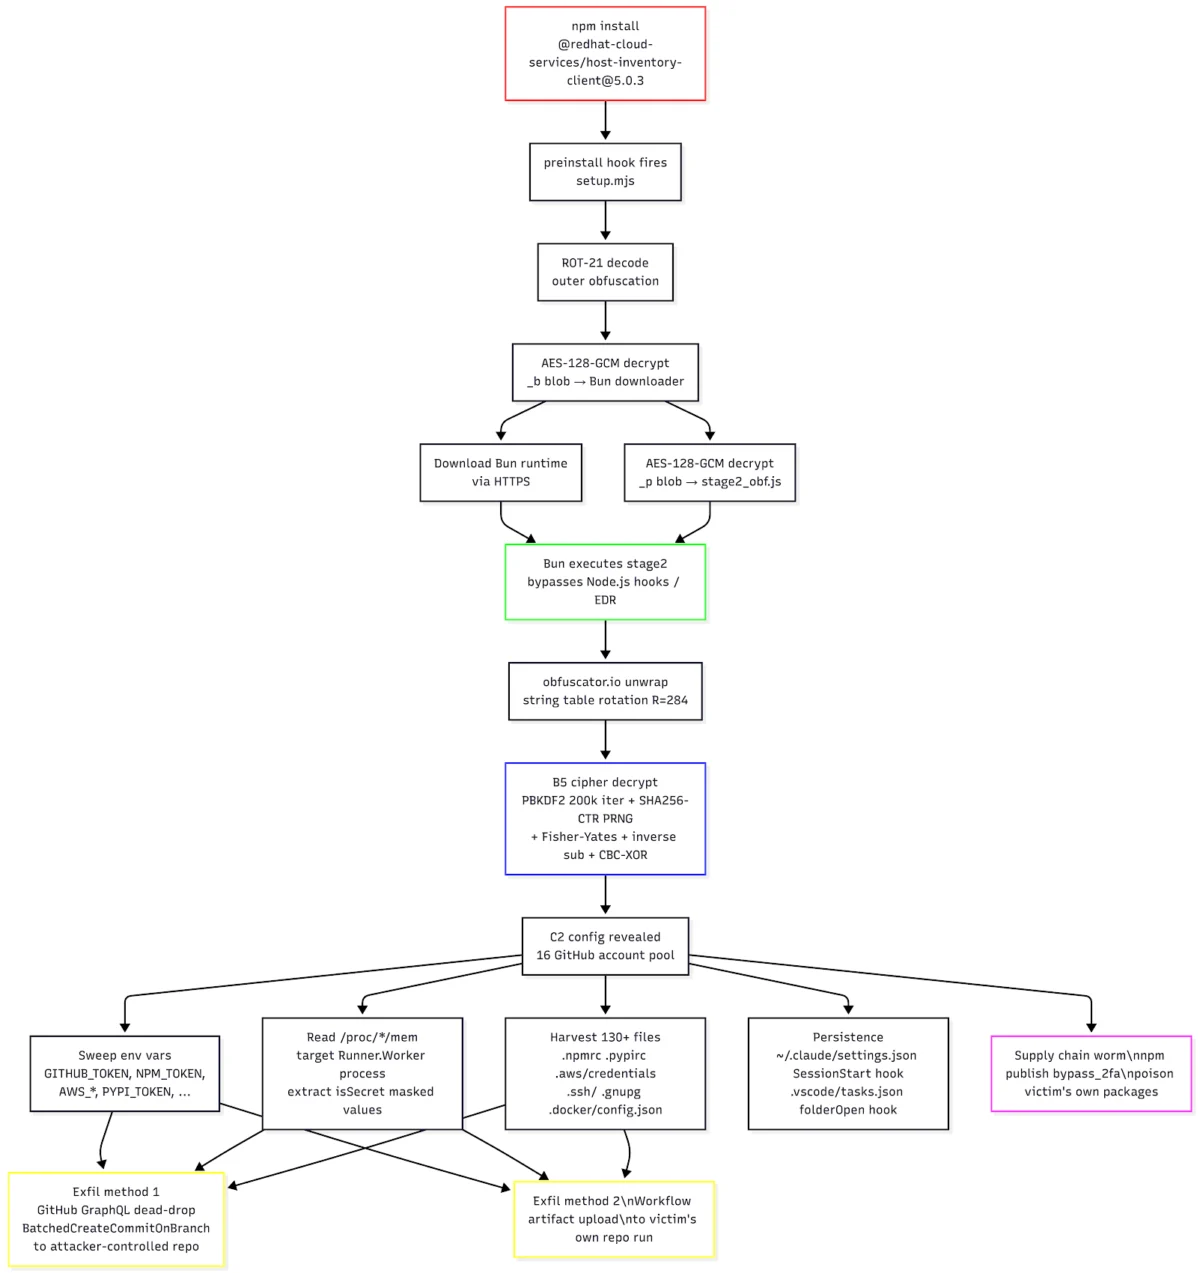
Miasma Supply Chain Attack Compromises Red Hat npm Packages with Credential-Stealing Worm
A sophisticated new supply chain attack campaign, codenamed Miasma, has been uncovered, significantly compromising @redhat-cloud-services…
Cybersecurity & Digital Privacy
Continue Reading
Threat Actors Exploit FortiClient EMS Vulnerability to Deliver Credential-Stealing Malware, Highlighting Critical Endpoint Security Risks
Threat actors are continuing to actively exploit a critical, now-patched security flaw impacting FortiClient Endpoint…
Cybersecurity & Digital Privacy
Continue Reading
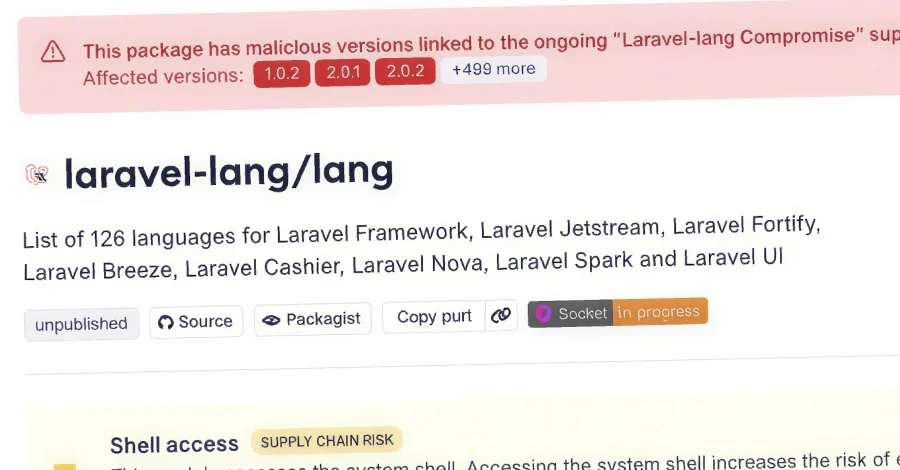
Laravel-Lang Targeted in Sophisticated Supply Chain Attack Delivering Comprehensive Credential-Stealing Framework
Cybersecurity researchers have recently identified and flagged a sophisticated software supply chain attack campaign that…
Cybersecurity & Digital Privacy
Continue Reading
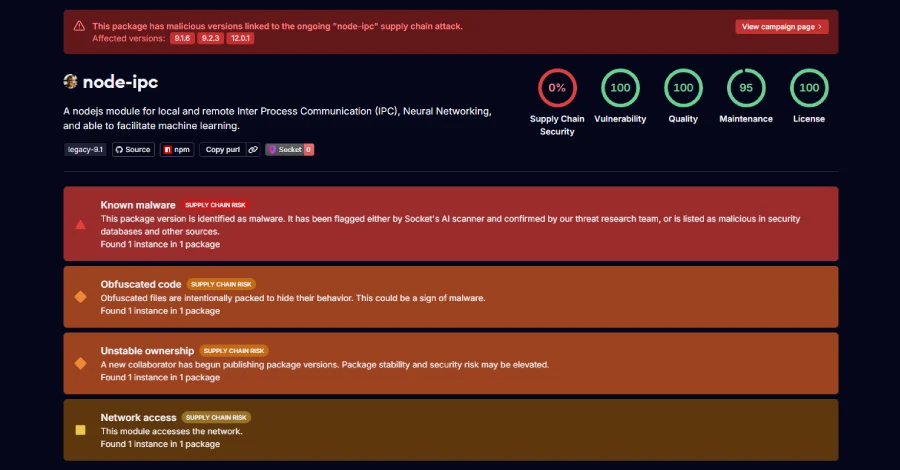
Cybersecurity Researchers Uncover Sophisticated Credential Stealer in Compromised Node-IPC npm Package
Cybersecurity researchers are sounding a definitive alarm regarding a highly sophisticated and deeply concerning malicious…
Blockchain & Web3

Continue Reading
Microsoft Threat Intelligence Confirms Malicious Code Injected into Mistral AI Software Package, Exposing Developers to Credential Theft
Microsoft Threat Intelligence has confirmed that malicious code was deliberately inserted into a Mistral AI…
