
The digital security landscape is currently grappling with the fallout from a severe security vulnerability…
Tag: Security
Cybersecurity & Digital Privacy

Continue Reading
Star Blizzard Escalates Cyber Espionage Campaigns Targeting Ukraine-Affiliated Organizations Through Sophisticated Malware Delivery
The Russian state-sponsored threat actor known as Star Blizzard has significantly ramped up its cyber-espionage…
Cybersecurity & Digital Privacy
Continue Reading
Massive Data Breach at French Tax Authority Exposes Hundreds of Thousands of Taxpayers and Businesses
A significant cybersecurity failure at France’s tax administration, the Direction Générale des Finances Publiques (DGFIP),…
Network Infrastructure & 5G

Continue Reading
Wallapop integrates Bizum into its payment ecosystem to streamline transactions and enhance user security
The integration of Bizum as a native payment method within the Wallapop platform marks a…
Cybersecurity & Digital Privacy
Continue Reading
Branch Target Reuse: A New Spectre-v2 Vulnerability Exposes Modern CPU Architectures to JIT-Based Attacks
A team of researchers from the VUSec lab and Scuola Superiore Sant’Anna has unveiled a…
Cybersecurity & Digital Privacy
Continue Reading
Dutch authorities arrest former cybersecurity professional linked to notorious ShinyHunters hacking collective
Dutch law enforcement authorities have officially confirmed the apprehension of a 24-year-old Amsterdam resident in…
Cybersecurity & Digital Privacy
Continue Reading
Microsoft Warns of Stealthy NeedyMantis Malware Maintaining Persistent Access in Targeted Global Intrusions
Microsoft has issued a comprehensive technical advisory regarding a sophisticated, long-term post-compromise malware family dubbed…
Cybersecurity & Digital Privacy
Continue Reading
Apple Patches CoreGraphics Flaw Possibly Exploited in Targeted Attacks
The technology giant issued a critical security patch to remediate a high-severity vulnerability, designated as…
Cybersecurity & Digital Privacy
Continue Reading
JADEPUFFER Threat Actor Orchestrates AI-Driven Destructive Attacks Against Microsoft Azure Cloud Environments
The emergence of JADEPUFFER, a sophisticated threat actor tracked by Microsoft as Storm-3168, represents a…
Cybersecurity & Digital Privacy
Continue Reading
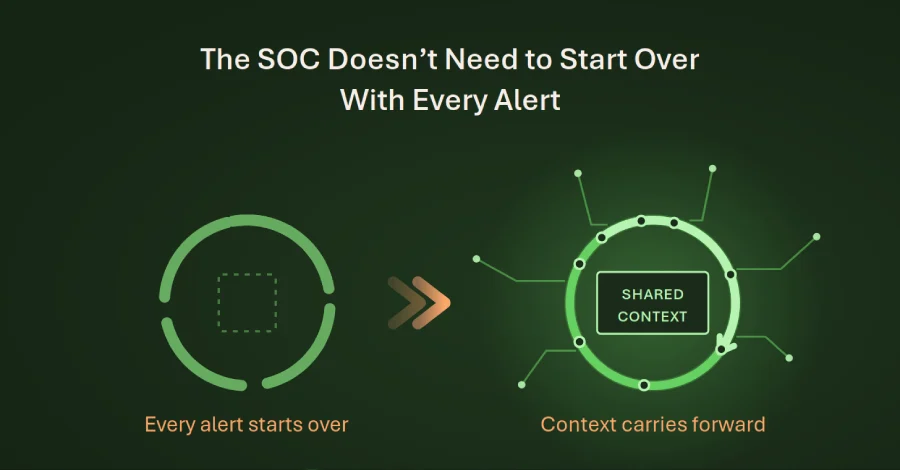
The Evolution of Cyber Warfare: Why AI is Rewriting the Rules of Engagement for Attackers and Defenders
Security leaders have spent the better part of the last two years debating whether generative…
