
The China-linked cyber espionage and ransomware group known as Warlock continues to pose a significant…
Tag: target
Digital Transformation & Strategy

Continue Reading
JD Sports Fashion Unveils Digital Overhaul to Target Gen Z Through Agentic Commerce and MACH Architecture
Global sportswear giant JD Sports Fashion is fundamentally rethinking how it reaches digital-native consumers, transitioning…
Cybersecurity & Digital Privacy

Continue Reading
Branch Target Reuse: A New Spectre-v2 Vulnerability Exposes Modern CPU Architectures to JIT-Based Attacks
A team of researchers from the VUSec lab and Scuola Superiore Sant’Anna has unveiled a…
Space & Satellite Tech

Continue Reading
SES Unveils Next-Generation Multi-Orbit Strategy and MeoSphere Program to Target 2030 Deployment
The satellite communications sector is undergoing a profound structural evolution, driven by surging global bandwidth…
Cybersecurity & Digital Privacy
Continue Reading
Critical Security Flaw in Issabel Framework Under Active Exploitation as Threat Actors Target Unified Communications Systems
A critical security vulnerability identified within the Issabel Framework, an open-source platform widely deployed for…
Cybersecurity & Digital Privacy
Continue Reading
KREMLIN Banking Malware Leverages Blockchain Infrastructure to Target Financial Institutions Across Brazil
Cybersecurity researchers at Elastic Security Labs have uncovered a sophisticated and highly resilient banking malware…
Cybersecurity & Digital Privacy
Continue Reading
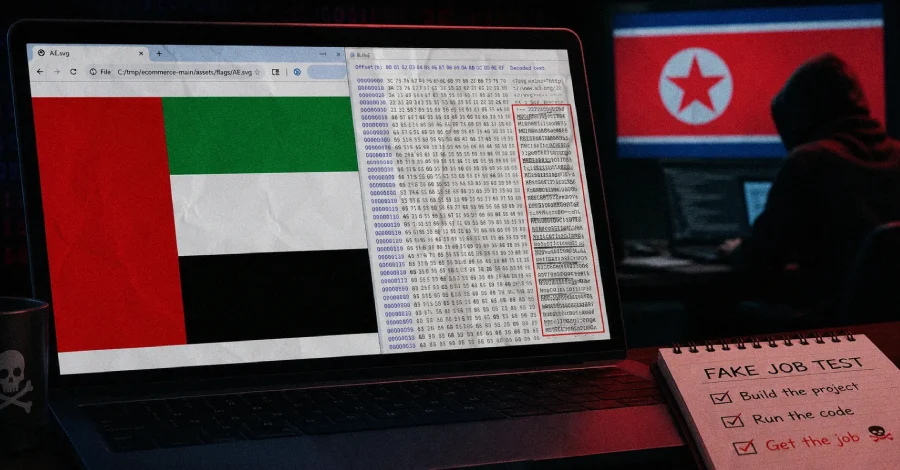
North Korean Cyber Actors Employ Sophisticated Steganography in SVG Files to Target Developers via Fake Job Offers
North Korean threat actors, operating under the moniker REF9403 and linked to the persistent "Contagious…
Space & Satellite Tech
Continue Reading
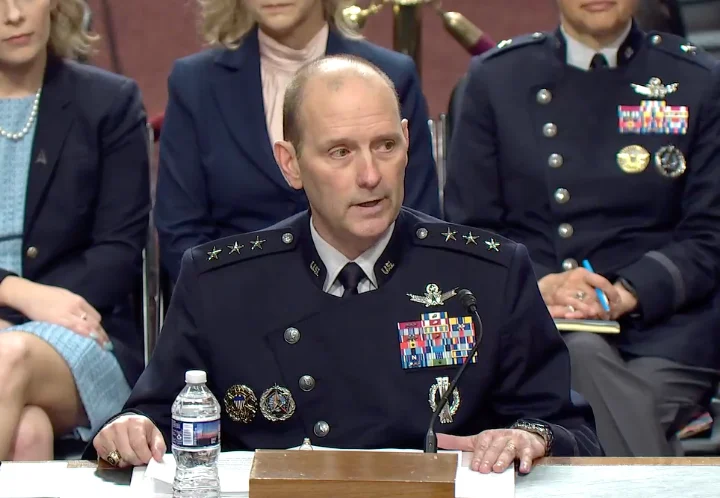
Space Force Chief Nominee Schiess Counts Moving Target Indication Among Top Priorities
United States Space Force Lt. Gen. Douglas Schiess appeared before the Senate Armed Services Committee…
Cybersecurity & Digital Privacy
Continue Reading
Coordinated GitHub API Enumeration Campaigns Target Corporate Assets, Warns Datadog Security Labs
Datadog Security Labs has issued a significant warning regarding a series of "overlapping campaigns" systematically…
Cybersecurity & Digital Privacy
Continue Reading
Active Exploitation Attempts Target Critical Gitea Docker Vulnerability CVE-2026-20896
Threat actors are actively attempting to exploit a recently patched critical security flaw, identified as…
